

312-50v11 문제 16
권한이 없는 사람이 점심 러시 이후에 직원 출입구를 통해 직원을 따라 건물에 들어갑니다. 개인이 방금 수행한 위반 유형은 무엇입니까?
312-50v11 문제 17
Bob은 클라이언트 중 한 명을 위해 암호 평가를 수행하고 있습니다. Bob은 보안 정책이 적절하지 않다고 의심합니다.
그는 또한 그가 평가하고 있는 회사 전체에서 취약한 암호가 일반적일 것이라고 의심합니다. Bob은 암호 취약점과 키 로거에 대해 잘 알고 있습니다.
다음 옵션 중 Bob이 클라이언트 호스트 및 서버에서 암호를 검색하기 위해 채택할 수 있는 방법을 가장 잘 나타내는 것은 무엇입니까?
그는 또한 그가 평가하고 있는 회사 전체에서 취약한 암호가 일반적일 것이라고 의심합니다. Bob은 암호 취약점과 키 로거에 대해 잘 알고 있습니다.
다음 옵션 중 Bob이 클라이언트 호스트 및 서버에서 암호를 검색하기 위해 채택할 수 있는 방법을 가장 잘 나타내는 것은 무엇입니까?
312-50v11 문제 18
전문 해커인 클라크는 경쟁사에 대한 민감한 정보를 은밀하게 수집하는 조직에 고용되었습니다. Clark은 Whole Footprinting을 사용하여 대상 조직의 서버 IP 주소를 수집합니다.
또한 그는 대상 조직의 네트워크 범위와 같은 정보를 검색하고 네트워크에서 사용되는 네트워크 토폴로지 및 운영 체제를 식별하기 위해 온라인 도구에 대한 입력으로 서버 IP 주소를 입력했습니다. 위의 시나리오에서 Clark이 사용하는 온라인 도구는 무엇입니까?
또한 그는 대상 조직의 네트워크 범위와 같은 정보를 검색하고 네트워크에서 사용되는 네트워크 토폴로지 및 운영 체제를 식별하기 위해 온라인 도구에 대한 입력으로 서버 IP 주소를 입력했습니다. 위의 시나리오에서 Clark이 사용하는 온라인 도구는 무엇입니까?
312-50v11 문제 19
개발 중인 웹 애플리케이션을 테스트하는 동안 웹 서버가 다음을 제대로 무시하지 않는 것을 발견했습니다.
"dot dot slash"(../) 문자열 대신 서버의 폴더 구조 파일 목록을 반환합니다.
이 시나리오에서는 어떤 종류의 공격이 가능합니까?
"dot dot slash"(../) 문자열 대신 서버의 폴더 구조 파일 목록을 반환합니다.
이 시나리오에서는 어떤 종류의 공격이 가능합니까?
312-50v11 문제 20
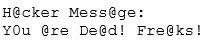
Joseph was the Web site administrator for the Mason Insurance in New York, who's main Web site was located at www.masonins.com. Joseph uses his laptop computer regularly to administer the Web site. One night, Joseph received an urgent phone call from his friend, Smith. According to Smith, the main Mason Insurance web site had been vandalized! All of its normal content was removed and replaced with an attacker's message ''Hacker Message: You are dead! Freaks!" From his office, which was directly connected to Mason Insurance's internal network, Joseph surfed to the Web site using his laptop. In his browser, the Web site looked completely intact.
No changes were apparent. Joseph called a friend of his at his home to help troubleshoot the problem. The Web site appeared defaced when his friend visited using his DSL connection. So, while Smith and his friend could see the defaced page, Joseph saw the intact Mason Insurance web site. To help make sense of this problem, Joseph decided to access the Web site using hisdial-up ISP. He disconnected his laptop from the corporate internal network and used his modem to dial up the same ISP used by Smith. After his modem connected, he quickly typed www.masonins.com in his browser to reveal the following web page:
훼손된 웹 사이트를 본 그는 전화 접속 회선을 끊고 내부 네트워크에 다시 연결한 다음 SSH(Secure Shell)를 사용하여 웹 서버에 직접 로그인했습니다. 그는 전체 웹 사이트에 대해 Tripwire를 실행하고 서버의 모든 시스템 파일과 모든 웹 콘텐츠가 손상되지 않았음을 확인했습니다. 공격자는 이 해킹을 어떻게 수행했습니까?
No changes were apparent. Joseph called a friend of his at his home to help troubleshoot the problem. The Web site appeared defaced when his friend visited using his DSL connection. So, while Smith and his friend could see the defaced page, Joseph saw the intact Mason Insurance web site. To help make sense of this problem, Joseph decided to access the Web site using hisdial-up ISP. He disconnected his laptop from the corporate internal network and used his modem to dial up the same ISP used by Smith. After his modem connected, he quickly typed www.masonins.com in his browser to reveal the following web page:
훼손된 웹 사이트를 본 그는 전화 접속 회선을 끊고 내부 네트워크에 다시 연결한 다음 SSH(Secure Shell)를 사용하여 웹 서버에 직접 로그인했습니다. 그는 전체 웹 사이트에 대해 Tripwire를 실행하고 서버의 모든 시스템 파일과 모든 웹 콘텐츠가 손상되지 않았음을 확인했습니다. 공격자는 이 해킹을 어떻게 수행했습니까?